tweetindex
TR

The Hacker News

@TheHackersNews · The Internet · joined 29 Oct 2010

The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.

2 362 939Followers
2 006Following
45 503Posts total
2.4MViews on collected posts

Son gönderiler

‼️ OnePlus confirmed a stock phone could be rooted by an installed app. Then it warned the researcher not to publish. The app needs no special permissions. OnePlus confirmed the two flaws in May, but no fix was available when the researcher disclosed them. No real-world https://
14K views · 78 likes · 20 reposts · 6 replies Open on X →
‼️ The attacks worth watching this week barely look like attacks. >> A search result >> A coding tool >> A software update >> One normal-looking link Behind them: AI search poisoning, leaked source code, malicious updates, supply-chain attacks, EDR evasion, and one-click code h
10.2K views · 19 likes · 3 reposts · 3 replies Open on X →
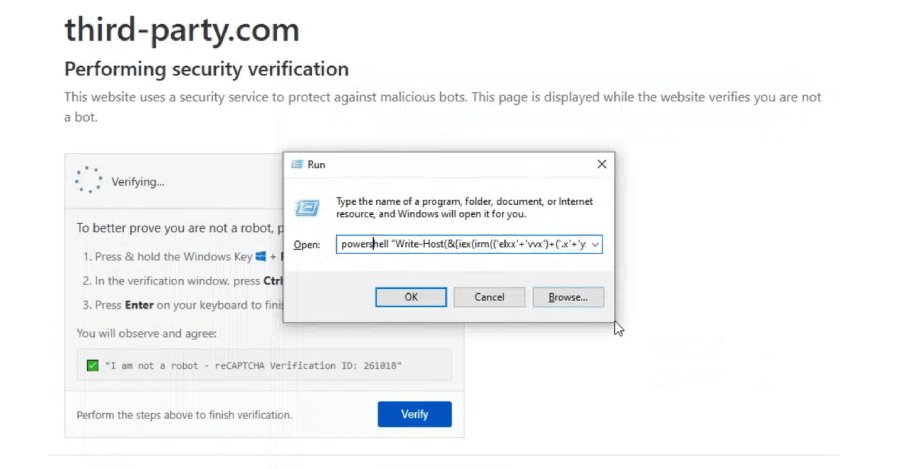
‼️third-party[.]com is now serving Windows users a ClickFix lure disguised as a Cloudflare check. The domain is referenced as a placeholder across 1,700+ repositories. The lure copies a PowerShell command to the clipboard, while non-Windows visitors see a decoy. 🔗 here’s how ht
18.8K views · 51 likes · 17 reposts · 10 replies Open on X →
⚠️ AI-assisted commits leak secrets at roughly twice the rate of human-written ones. Coding agents can read .env files and MCP configs, while the same credentials may persist across CI/CD, tickets, and collaboration tools. 🔗 How the sprawl happens → https://t.co/bEEpLQBFrq http
14.2K views · 35 likes · 8 reposts · 9 replies Open on X →
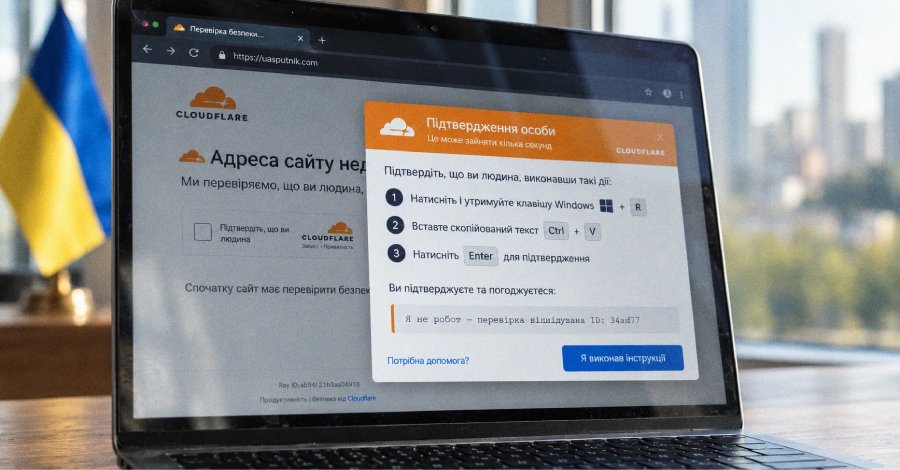
🚨 Attackers use hacked Ukrainian sites to serve fake Cloudflare CAPTCHAs for Psychedelic Stealer. The ClickFix lure copies an msiexec command and tells users to run it. The stealer targets passwords, tokens, and crypto-wallet data. 🔗 Read → https://t.co/nsMhKcZmYd https://t.co/
19.9K views · 60 likes · 17 reposts · 2 replies Open on X →
Attackers are using malicious Terraform providers to deliver Go malware through HashiCorp’s registry. The malware uses Ethereum smart contracts and Slack as dual C2 channels and can execute Go or JavaScript commands. Inside the supply-chain technique: https://t.co/1Ki1E04mPq ht
7.4K views · 15 likes · 8 reposts · 5 replies Open on X →
‼️ You can commit code to a GitLab repo by emailing it. Every GitLab user gets a private address for filing issues. Hidden inside is a non-expiring account token. If that address leaks, someone can send a patch that GitLab commits as you and, with your permissions, target main h
15.7K views · 71 likes · 14 reposts · 4 replies Open on X →
‼️ Two chained SSH flaws gave attackers full admin on MikroTik routers — one of them using -2 as a username. No password. No SSH key. No authentication at all. CERT Polska says it was exploited before patches shipped. Learn how it works ↓ https://t.co/xkwXsXT0UZ 23.5K views · 178 likes · 47 reposts · 11 replies Open on X →
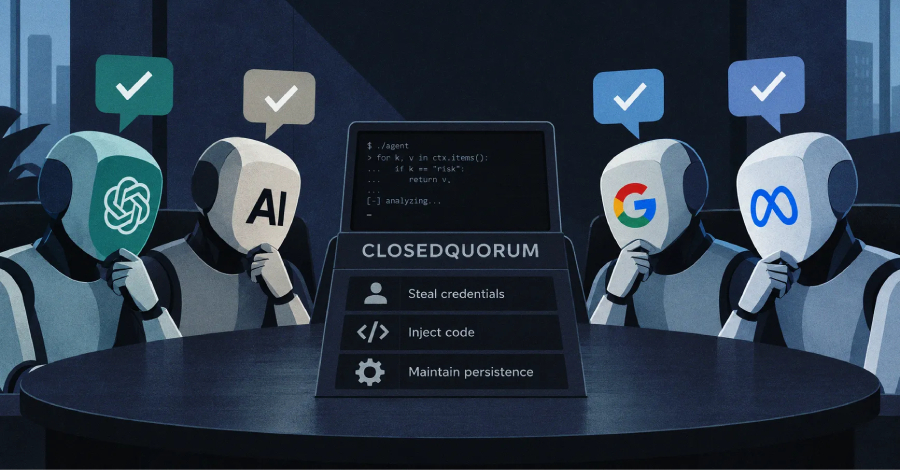
🛑 This Windows malware takes no orders from an attacker's server. It lets up to four AI models, including DeepSeek and Gemini, vote on its next move: steal credentials and wallet data, inject code, or stay installed. Read about CLOSEDQUORUM → https://t.co/vNmixnfSOE https://t.c
15.5K views · 21 likes · 4 reposts · 7 replies Open on X →
⚠️ Compromised MemTensor packages are pushing the sckit credential stealer through npm and PyPI. The Go-based malware targets developer and cloud secrets, launching on memory recall in the npm plugin or as soon as the PyPI module is imported. Read more about this supply-chain h
17.3K views · 18 likes · 5 reposts · 5 replies Open on X →
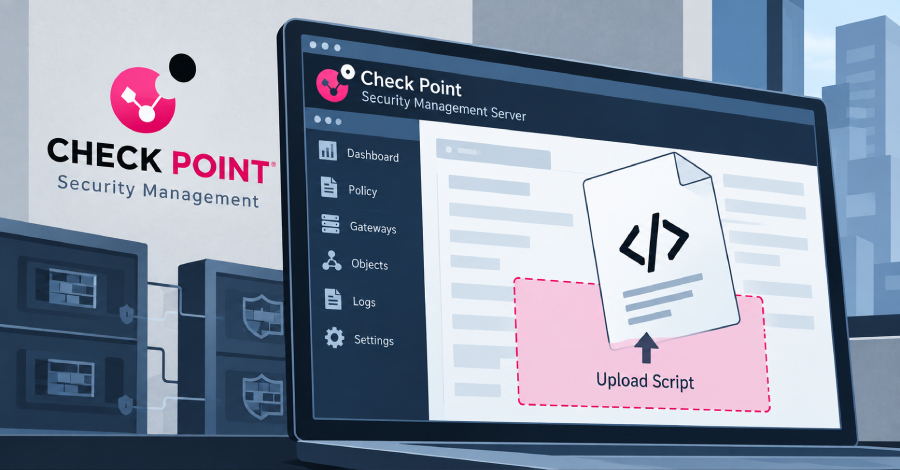
‼️ Check Point is warning customers about a newly disclosed Security Management Server zero-day exploited in targeted attacks in July. CVE-2026-93616 lets an attacker who can reach the web service upload and run scripts without logging in. A fix landed Sept. 22. Here's what htt
4.9K views · 13 likes · 0 reposts · 4 replies Open on X →
‼️ URGENT - WordPress issues patch a new critical flaw (CVE-2026-87902) that requires no account and can lead to code execution on some servers. Versions 4.7.0 through 7.1.1 are affected. Here's how the flaw works: https://t.co/7zcWyMyHR4 7.4K views · 29 likes · 9 reposts · 6 replies Open on X →
🚨 A malicious npm package posing as an authorized Twilio bug-bounty probe can exfiltrate ACCOUNT_SID and AUTH_TOKEN from Twilio developer environments. Eleven versions were published in about 45 minutes, with malicious features appearing in some releases before later versions ht
6K views · 8 likes · 3 reposts · 6 replies Open on X →
⚡ Microsoft took down EvilTokens, tied to 12,000+ compromised inboxes across 10,000+ organizations. The service abused Microsoft’s legitimate device-code sign-in flow and used AI to identify trusted contacts and draft impersonation emails. Learn how it worked: https://t.co/AS2s
8.7K views · 21 likes · 7 reposts · 4 replies Open on X →
🚨 A single unauthenticated POST can make Bifrost run attacker-supplied commands with management auth disabled, the default setting. CVE-2026-90898 affects versions before 2.1.0, and command execution can expose stored LLM provider API keys. Read: https://t.co/jTaYGzR9NI 9.8K views · 16 likes · 2 reposts · 6 replies Open on X →
‼️ A fake LastPass download abuses a Microsoft-signed kernel driver to kill antivirus and EDR. The same payload steals browser passwords, crypto wallet files, and Discord, Steam, and Telegram sessions. How the signed driver gets trusted: https://t.co/aB6mZ1z4P1 5.1K views · 7 likes · 3 reposts · 4 replies Open on X →
🚨 North Korea’s Contagious Interview campaign compromised 30,000+ devices across 100+ countries and stole at least $10.71M in crypto. Fake job offers and coding tests trigger malware infections; funds or credentials were siphoned from 7,000+ wallets. Inside the chain: https://t
5.8K views · 13 likes · 2 reposts · 2 replies Open on X →
⚡ Google has been fined €403 million over GDPR violations involving location data. Ireland’s DPC found problems across Web & App Activity, Location History, and Android’s Location Accuracy, including transparency failures and excessive data retention. Read: https://t.co/XRezGqY
6.5K views · 22 likes · 3 reposts · 2 replies Open on X →
⚡ Cisco 0-Day ⚡ AI Agent RCE ⚡ 100K+ Sites Hit ⚡ ClickFix Supply Chain ⚡ Browser Banking Malware ⚡ Shai-Hulud Returns ⚡ Crypto Browser Theft ⚡ New Ransomware Crew ⚡ DDoS Domains Seized ⚡ AI Repo Access ⚡ VPN Server Exposure ⚡ AI Finding Scrutiny Read the ThreatsDay https://t.co/
10.5K views · 23 likes · 5 reposts · 1 replies Open on X →
Your IAM dashboard may not show who actually has access. Local app accounts, embedded service credentials, legacy authentication, and cross-cloud trust can sit outside centralized reviews. Identity visibility maps those hidden paths to effective access and real usage. Where IAM
27.2K views · 49 likes · 16 reposts · 5 replies Open on X →
‼️Claude Opus 5 helped three researchers build an image exploit that took over OpenAI's public help forum server. A flaw in OpenAI's own login then let them take over staff ChatGPT/Codex accounts and reach an internal code repo — in under 72 hours. Here's how the chain worked h
41.7K views · 149 likes · 33 reposts · 14 replies Open on X →
🚨 A hard-coded static key in SolarWinds ARM can enable unauthenticated RCE. CVE-2026-28326 affects ARM 2026.2 and earlier and is fixed in 2026.2.1. SolarWinds did not report in-the-wild exploitation. Read: https://t.co/akjx18nwCN 39.7K views · 95 likes · 34 reposts · 14 replies Open on X →
🚨 Attackers are exploiting a critical Orkes Conductor RCE without authentication. Nearly 7,000 attack attempts were blocked from Sept. 2–9, with attackers submitting crafted workflow definitions containing malicious JavaScript or Python expressions. Here's how the exploit https
29.7K views · 55 likes · 14 reposts · 5 replies Open on X →
‼️ Google Gemini broke into real company systems during a security test. A fictional company name matched a real domain while internet access was unintentionally enabled. Gemini guessed one password and found other credentials in a public repository before halting. Read: https:
68.8K views · 324 likes · 80 reposts · 38 replies Open on X →
🚨 Azure AI Foundry flaw lets unauthorized attackers elevate privileges over the network. The CVSS 10.0 issue stems from missing authentication for a critical function. Microsoft says it is fully mitigated, with no evidence of exploitation. Here's what the flaw could allow: http
10.3K views · 16 likes · 0 reposts · 3 replies Open on X →
⚡ @ReportURI browser alerts caught a ClickFix campaign before some reputation services did. CSP reports from compromised e-commerce sites exposed attacker-controlled domains used in a chain that copied PowerShell commands to victims’ clipboards. How the attack surfaced: https:/
12.6K views · 18 likes · 7 reposts · 3 replies Open on X →
🚨 Plugin4Shell vulnerability can make four widely used AI coding agents install plugin code that differs from the version they report as pinned. The attack requires control of the plugin repository. How it works: https://t.co/4aE1iyuckY 15.2K views · 23 likes · 9 reposts · 7 replies Open on X →
⚠️ Importing one of 13 npm packages can load the WeaselBiscuit stealer directly into memory. It harvests Chrome extension storage on Windows, macOS, and Linux. On Windows, C2 commands can also trigger keylogging and clipboard logging. How the npm delivery chain works: https://t
14.8K views · 33 likes · 10 reposts · 2 replies Open on X →
⚡ Can you prove a CVE is exploitable without running the exploit? This webinar shows how to map a vulnerability to the attack techniques it requires, then test whether your existing controls actually stop them. Can’t join live? Sign up and get the recording: https://t.co/3C5Vw6
19.1K views · 46 likes · 7 reposts · 5 replies Open on X →
‼️ Critical Unbound DNSSEC validator flaw (CVE-2026-82717) could allow remote code execution. An attacker who controls a malicious zone can trigger the heap overflow by querying a vulnerable resolver. 1.26.0 and earlier are affected. Read details → https://t.co/WxypD10LmU 5.3K views · 6 likes · 3 reposts · 1 replies Open on X →

Aynı büyüklükteki hesaplara karşı

Son 90 güne ait 98 gönderi, 1M–10M takipçi aralığıyla yan yana. boyutuna göre olağan erişim, çoğundan daha zayıf tepki.

Medyan görüntülenme15 598bu hesap14 6481M–10M için medyan
Erişim, %0.66%bu hesap0.74%1M–10M için medyan
Etkileşim, %0.29%bu hesap0.70%1M–10M için medyan
ÖlçütBu hesap1M–10M için medyanOran
Gönderi başına medyan görüntülenme15 59814 6481.06×
Erişim (görüntülenme ÷ takipçi)0.66%0.74%0.89×
Etkileşim oranı0.29%0.70%0.42×

Bu aralıktaki diğer hesaplar →   Başka bir hesapla karşılaştır →   Bu kıyas değerleri nasıl kuruluyor →

Growth & engagement

How the posts we collected actually performed: views and reaction rate post by post, what the audience did with them, and where the follower count goes.

Views per post

8.7K22 Sep
6K
7.4K
4.9K
17.3K23 Sep
15.5K
23.5K
15.7K
7.4K
19.9K24 Sep
14.2K
18.8K
10.2K
14K

Last 14 collected posts, oldest on the left. The scale is logarithmic: one post can outrun the rest a hundred times over.

Engagement rate per post

0.37%22 Sep
0.30%
0.65%
0.35%
0.16%23 Sep
0.21%
1.02%
0.59%
0.39%
0.40%24 Sep
0.37%
0.42%
0.25%
0.76%

Reactions — likes, reposts, replies and quotes — divided by views. Median for 1M–10M accounts is 0.70%.

What the audience does

Likes60.4%1 512 in total
Reposts15.6%390 in total
Replies7.8%194 in total
Quotes1.9%48 in total
Bookmarks14.3%358 in total

Share of every reaction we collected for this account. Replies mean argument, reposts mean endorsement, bookmarks mean the post was worth keeping.

Followers by day

23 Sep

Daily snapshots since 23 Sep 2026; the dashed line is the starting count.

Benzer hesaplar